CVE-2026-19607
This repository documents the vulnerability details and an exploit for CVE-2026-19607, discovered and responsibly reported by Anurag Mondal (7Ragnarok7) on 8th August, 2026.
Metrics
Description:
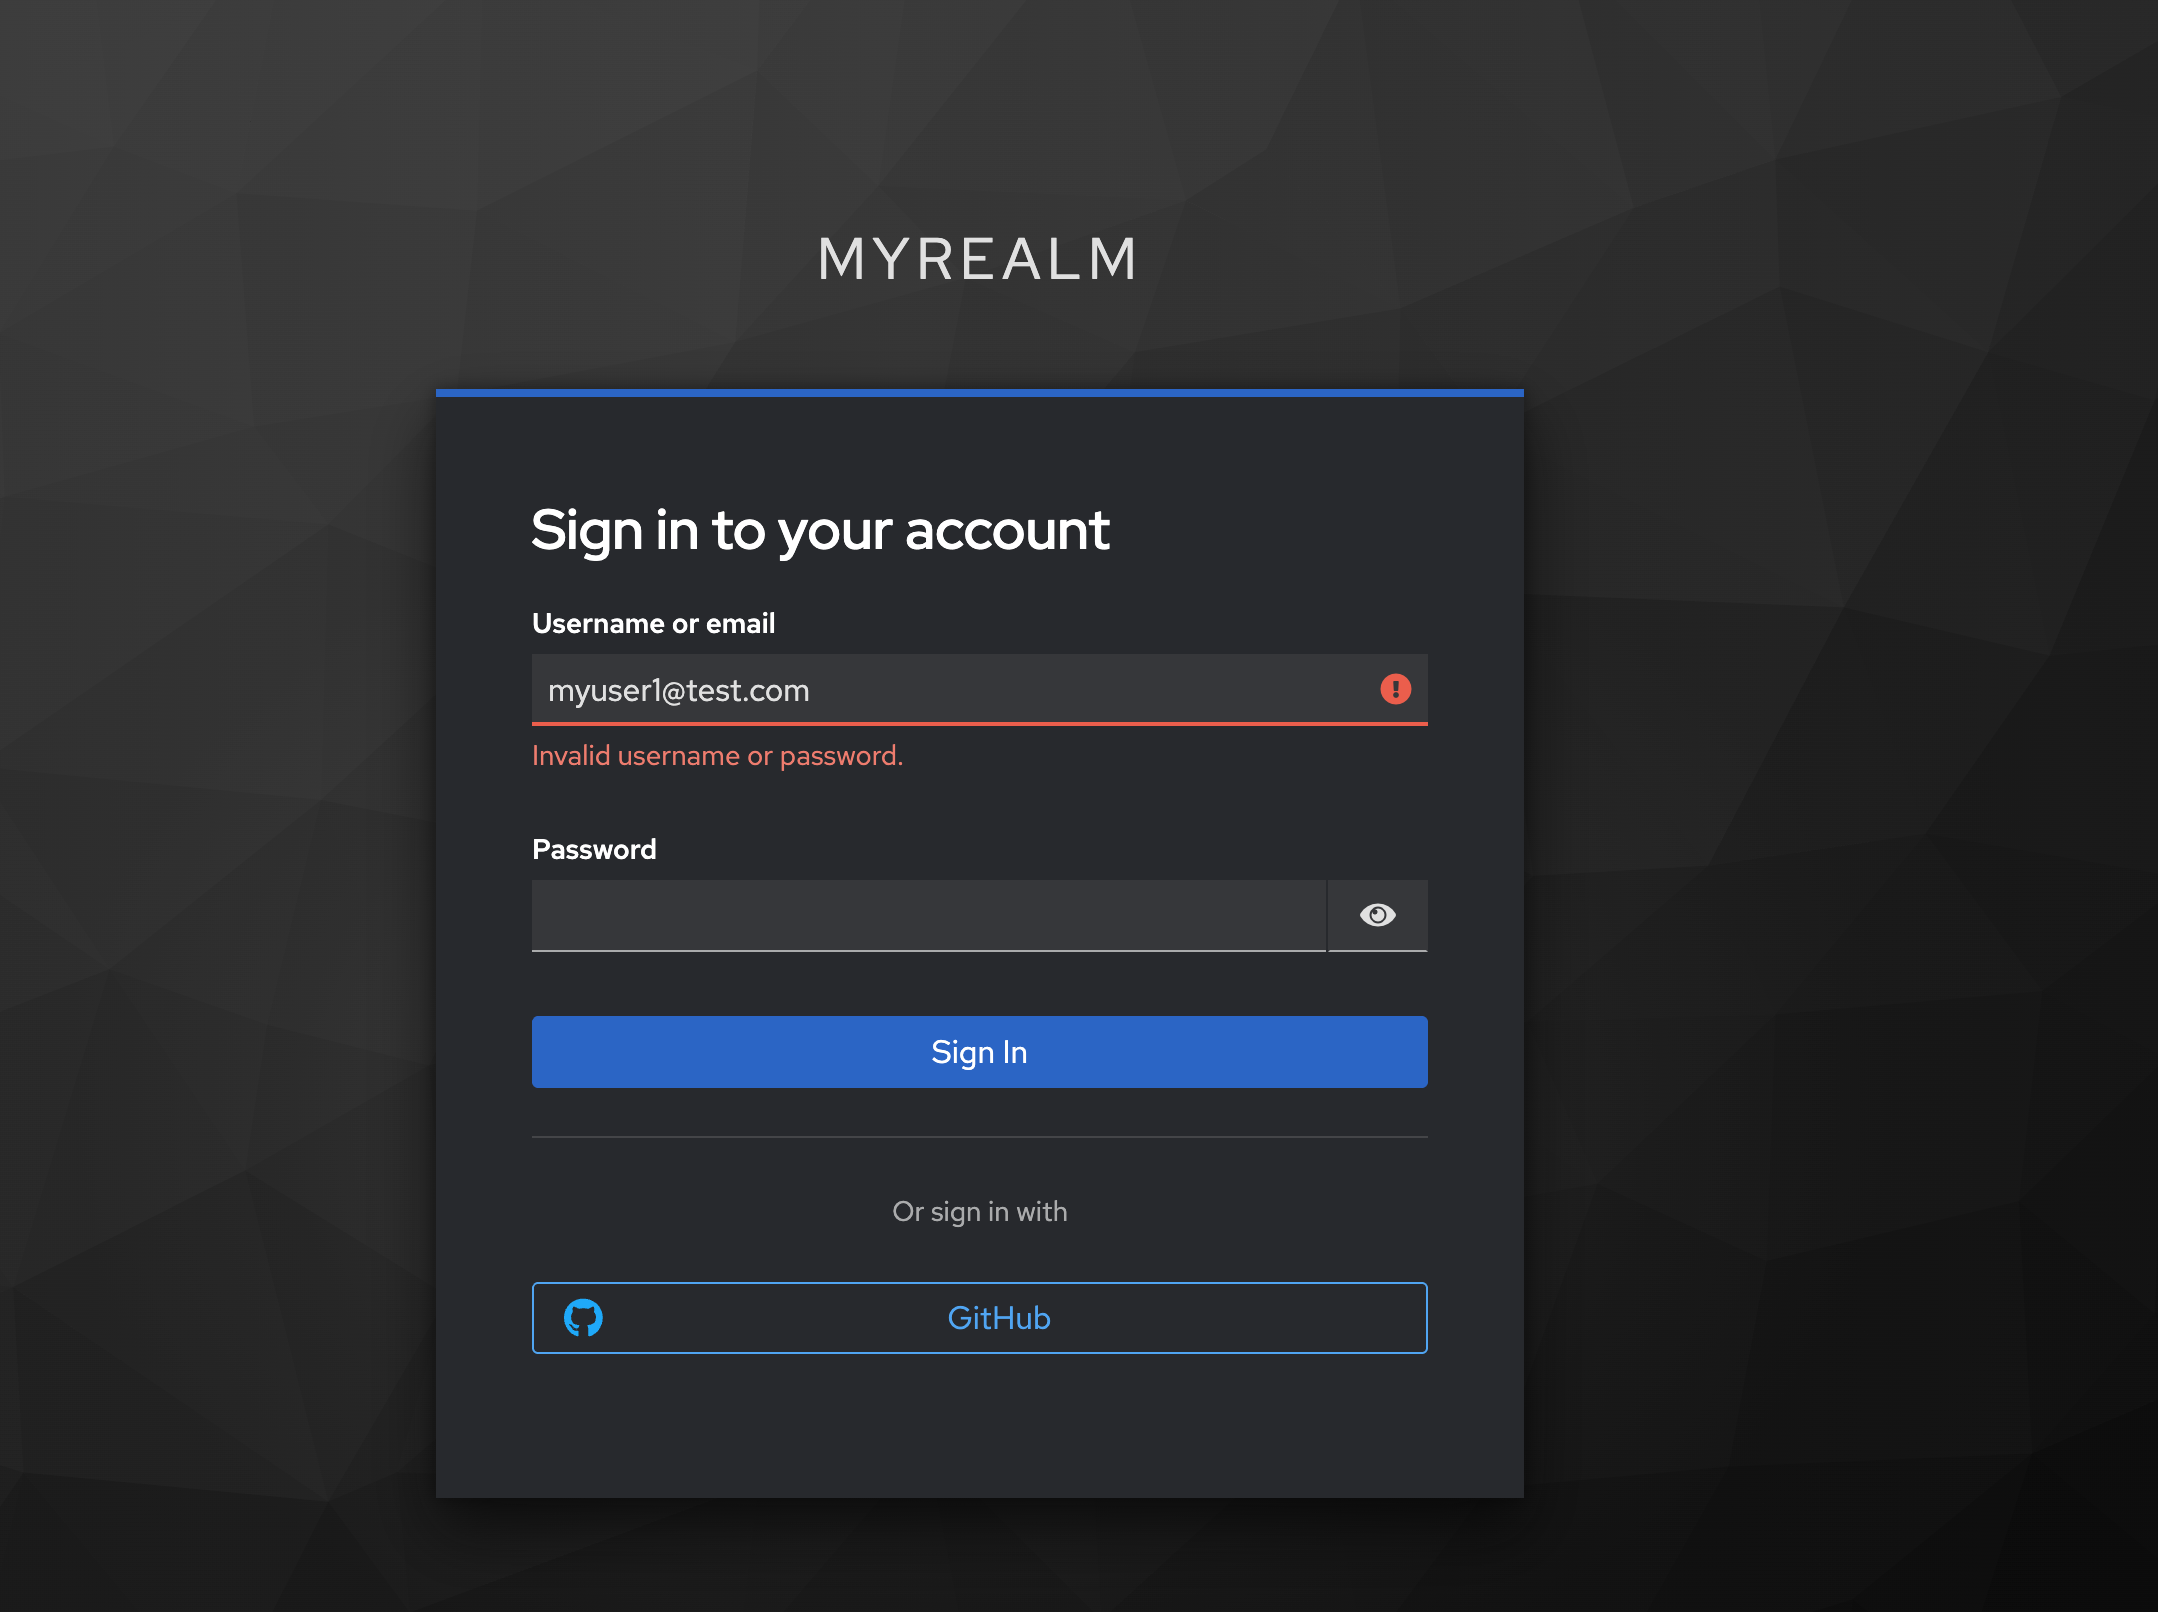
A flaw was discovered in Keycloak (versions <= 26.7.14, 26.4.16, and 26.6.7) in which an attacker can register using an email address that matches the username of any existing user when coming from a third-party login broker / IDP.
Impact:
The above behaviour will allow the attacker to take over the username of a victim account if the username is set as an email ID, and lock out the associated user from their account. All authentication attempts using the victim’s username will fail.
Advisory
- The official advisory by the project maintainer can be found at https://github.com/advisories/GHSA-h87q-rx56-87wm.
Proof of Concept / Exploit:
The Following is a proof of concept video which demonstrates the vulnerability details along with exploitation steps:
Important Links:
- https://7Ragnarok7.github.io/CVE-2026-19607/
- https://www.keycloak.org/2026/09/keycloak-2674-released
- https://access.redhat.com/security/cve/cve-2026-19607
- https://github.com/keycloak/keycloak/issues/52837
- https://github.com/advisories/GHSA-h87q-rx56-87wm
- https://bugzilla.redhat.com/show_bug.cgi?id=2514529
- https://www.cve.org/CVERecord?id=CVE-2026-19607